Melody Auth
- Platform
- Docker Self-hosted
- Licence
- MIT Open source
- Website
- auth.valuemelody.com/
- Source code
- github.com/ValueMelody/melody-auth
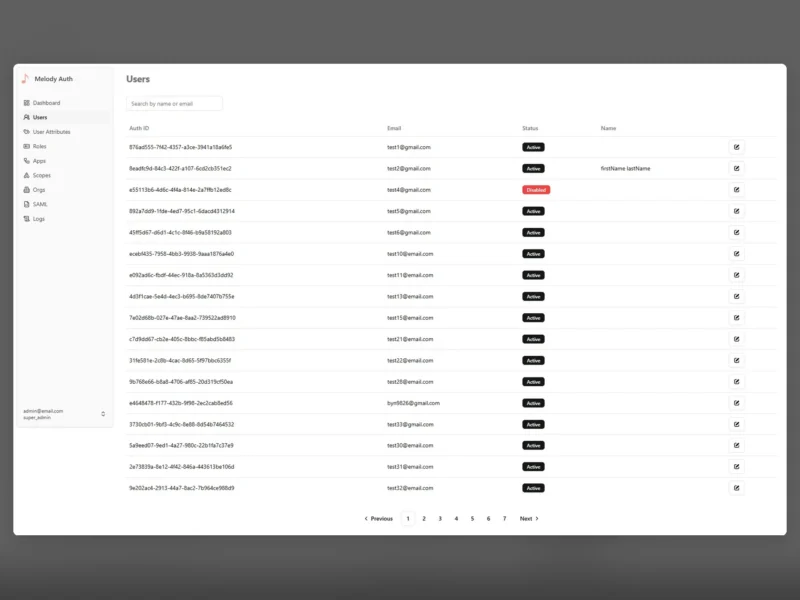
Melody Auth is a turnkey OAuth 2.0 and OpenID Connect server: a complete authentication backend you host yourself, with a sign-in and sign-up UI, an admin panel and client SDKs, rather than a library you have to wire into an existing framework. It is written in TypeScript under the MIT licence, and it deliberately targets two deployment shapes — Cloudflare Workers with D1 and KV for people who do not want to run servers at all, and plain Node.js with Redis and PostgreSQL for people who do.
Two ways to run it
The Cloudflare route deploys the auth server as a Worker, with D1 as the database and KV for session and cache state; the repository ships the bindings, migrations and setup notes needed to stand it up from a fresh account, which is what makes “in minutes” a realistic claim rather than a slogan. The Node.js route runs the same code as a conventional service against PostgreSQL and Redis, which is the path that supports the features Cloudflare’s runtime cannot provide, such as SAML single sign-on and SMTP mail delivery. A Docker Compose setup in devops/docker is the quickest way to try it locally.
What the auth server does
The server implements the OAuth 2.0 flows an application actually needs — authorize, token exchange, refresh token revocation, app consent, app scopes, userinfo and the OpenID configuration document — plus the surrounding account lifecycle: sign-in, passwordless sign-in, sign-up, sign-out, email verification, password reset and account linking. Access control is role-based, with per-user attributes you define yourself, and every screen can be localised. Policies decide which of those flows a given client app is allowed to offer, so a first-party app can require password plus MFA while a read-only dashboard allows a passwordless link.
External identity and single sign-on
Google, Facebook, GitHub, Discord and Apple sign-in are supported out of the box, alongside generic OIDC providers for anything else. SAML SSO is available for the Node.js deployment. Organisation support adds a second layer that the sign-in pages respect: per-organisation branding overrides, organisation users and organisation groups, so one instance can serve several tenants with their own look and their own membership without separate deployments.
Multi-factor, passkeys and brute-force protection
Second factors can be email codes, TOTP or SMS through Twilio, and users can enrol a passkey or generate recovery codes themselves; “remember this device” keeps a trusted browser unlocked for 30 days. MFA can be configured per app rather than only globally. Brute-force protection is applied to the flows that get attacked in practice — sign-in, password reset, email verification, change-email, and each MFA channel — and everything is logged, with separate email logs, SMS logs and sign-in logs visible in the admin panel.
Admin panel, API and SDKs
The admin panel is a Next.js application that doubles as the project’s full-stack reference implementation: it manages users, invites and impersonation, user attributes, apps and their banners, scopes, roles, organisations, SAML identity providers and logs, with custom roles able to gate access to the panel itself. Behind it sits a server-to-server REST API with Swagger documentation for backend integrations, and an embedded auth API for putting the sign-in flows inside your own UI. Frontend SDKs are published for React, Angular, Vue and plain JavaScript, all PKCE-based, with runnable examples for each including Next.js, React Native and Auth.js.
Before you commit
The trade-off is Cloudflare-shaped. The Workers deployment is genuinely low-maintenance, but D1 and KV bindings plus migrations are part of the setup, and SAML SSO and SMTP are Node.js-only, as is anything that needs a raw socket. Mail flows rely on a transactional provider (SendGrid, Mailgun, Brevo, Resend, Postmark or SMTP), and SMS on Twilio, so there is an external dependency before password reset or verification emails work. The project also states that its French translations were AI-generated and should be reviewed before production use. Development is active — releases and documentation changes land continuously — so pin a version and read the changelog for migration steps between majors.
Alternatives
- Keycloak — the heavyweight open source identity provider, far more protocols and admin surface, far more to operate
- authentik — self-hosted identity provider with a visual flow editor and proxy outpost model
- Zitadel — multi-tenant identity platform with a strong API-first design
- Logto — developer-facing OIDC provider with built-in sign-in experience customisation
- Rauthy — a single-binary OIDC provider in Rust, if you want one small process instead of a stack