Cerbos
- Platform
- Linux macOS Docker
- Licence
- Apache-2.0 Open source
- Website
- cerbos.dev/
- Source code
- github.com/cerbos/cerbos
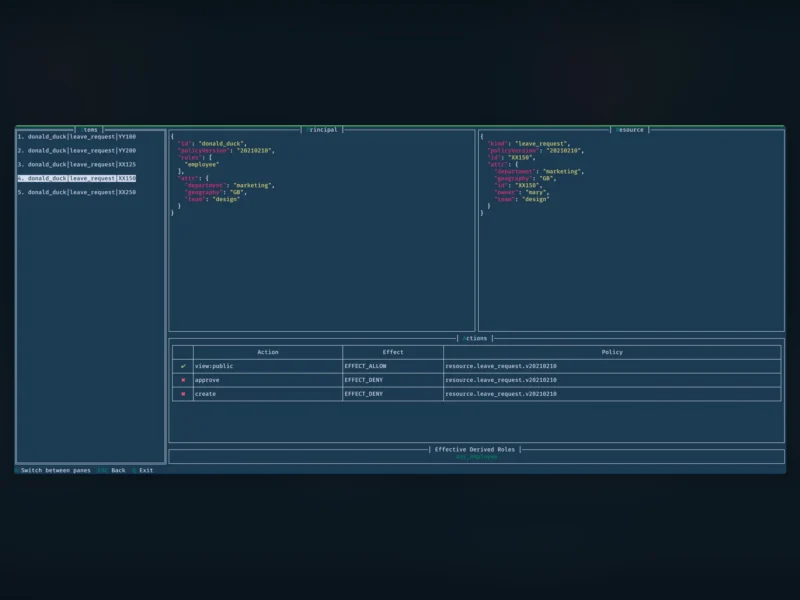
Cerbos is an authorization layer for applications, APIs and infrastructure: instead of scattering permission checks through your codebase, you write policy in YAML and ask a Policy Decision Point (PDP) whether a principal may perform an action on a resource. The PDP is a stateless Go service that runs as a container, a single binary, a Helm chart, a systemd unit or a Kubernetes sidecar, and answers two questions: “can this principal access this resource?” (CheckResources) and “which of the resources of kind X can this principal access?” (PlanResources).
How the policy model works
Every decision is a triple of principal (a user, service, bot or workload), action (view, edit, approve, delete…) and resource (the thing being protected). Policies are YAML files organised as resource policies, derived roles and principal policies, so a rule reads as “the owner may view this album when it is published” rather than a pile of role checks. Conditions are written in CEL against attributes on the principal, the resource and the request context, which is what makes attribute- and relationship-aware rules practical without a policy language of your own.
Features
- Policy as code — YAML policies stored on disk, in an S3/GCS bucket, in a Git repository or in SQLite, and hot-reloaded by the PDP; the same files go through your normal review and GitOps flow.
- Derived roles — roles computed at request time from context (team, department, ownership, resource flags) instead of being baked into static role lists.
- Schemas and validation — JSON schemas for principal and resource attributes, plus
cerbos compileandcerbos test(with a fixture “testdata” format) so policies fail in CI rather than in production. - Query planning —
PlanResourcesreturns a filter condition instead of a boolean, so a database query only fetches the rows the caller is allowed to see; adapters exist for Prisma and SQLAlchemy. - Decisions TUI —
cerbos decisionsrenders live decision logs in a terminal interface for debugging why a request was allowed or denied, including the matched policy and effective derived roles. - Policy test runner — table-driven tests describe principals, resources and expected effects, and run from the CLI in CI.
- Client SDKs — Go, Java, JavaScript, .NET, PHP, Python, Ruby and Rust, so the PDP speaks gRPC or HTTP to whatever your service is written in.
- Standards alignment — RBAC, ABAC and PBAC in one model, with an OpenID AuthZEN-compatible API surface.
Deployment
In Kubernetes, run the PDP as a sidecar next to the service that calls it (one hop, no shared database) or as a DaemonSet/Deployment service for the whole cluster; outside Kubernetes it runs as a systemd service or on AWS Lambda. Storage backends, audit logging and the gRPC/HTTP listeners are configured in a single YAML file, and anonymous telemetry can be disabled with CERBOS_NO_TELEMETRY=1. Linux and macOS builds plus official container images are published for the server and the cerbosctl CLI.
Open-core boundary
The self-hosted PDP in this repository is Apache-2.0 and complete on its own. Cerbos Hub is the vendor’s commercial SaaS control plane: collaborative policy playgrounds, distributing policy bundles to a fleet of PDPs, client-side/browser authorization bundles, and a hosted policy store. Hub is optional — policies can be managed entirely from Git without it — and the company sells it as a paid service, which is what makes this an open-core project rather than a fully open-source company.
Related tools
- Casdoor — open source identity and access management with permission management built in, if you want the IdP and the authorization console in one place.
- Keycloak — open source identity provider whose authorization services cover coarser, role- and resource-server-based policy.
- Authelia — forward-auth gateway for protecting self-hosted web apps, a complement to a fine-grained decision point inside the app.