CetusGuard
- Platform
- Docker Linux macOS Windows
- Licence
- MIT Open source
- Source code
- github.com/hectorm/cetusguard
CetusGuard is a small proxy that sits between the Docker daemon socket and the services that want to use it, and filters the API calls allowed through. Instead of handing a dashboard or a metrics agent full read and write access to a root daemon, you point the client at CetusGuard and give it a list of the endpoints that client may reach.
Why the daemon socket needs a guard
Unless it runs in rootless mode, the Docker daemon is root, and any process that can reach its API inherits that power: a container created with a host mount is a privilege escalation away from the whole machine. File permissions on the Unix socket only decide who may connect, not what they may do once connected. CetusGuard adds the missing layer, so a monitoring container can list containers and read events while being unable to create, delete or exec into anything.
How it works
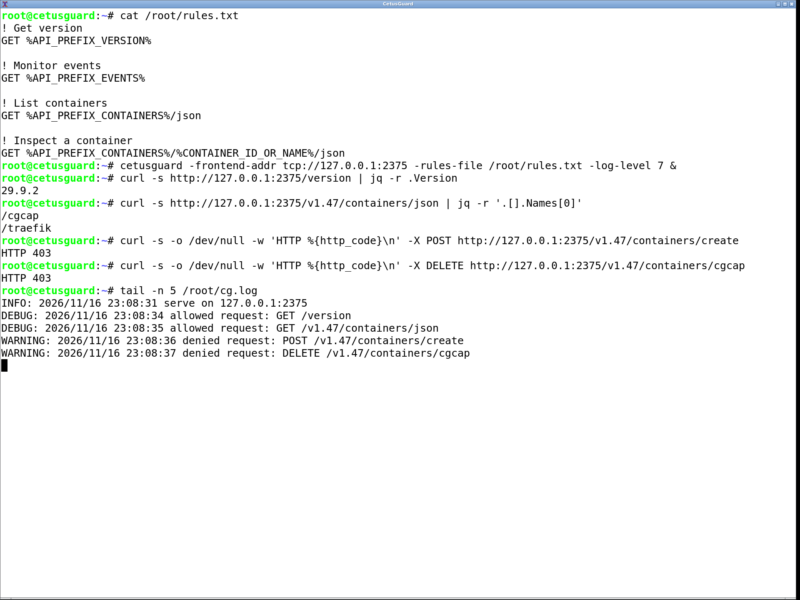
It listens on one or more frontend addresses, TCP or a Unix socket, with optional TLS on both sides, and checks every request’s method and target against its rules before forwarding the request to the real daemon. A call that matches no rule is refused with a 403 and a warning in the log, which makes the proxy’s own output the audit trail of everything a client tried to do.
Filter rules
A rule is an HTTP method list, whitespace, and a regular expression matched against the decoded path, or against path and sorted query when the pattern contains a question mark. The built-in rules already allow the harmless endpoints such as /_ping, /version and /info; every other endpoint stays closed until a rule opens it. Variables such as %API_PREFIX_CONTAINERS% expand to the versioned API prefix, so the same rule keeps working across API versions.
! List containers
GET %API_PREFIX_CONTAINERS%/json

! Inspect a container
GET %API_PREFIX_CONTAINERS%/%CONTAINER_ID_OR_NAME%/json

! Monitor events
GET %API_PREFIX_EVENTS%
Running it
CetusGuard ships as a container image on Docker Hub and the GitHub Container Registry, and as a statically linked binary for Linux, macOS and Windows. It works with Docker and with Podman, since the backend address is just a socket to connect to.
docker run --rm -p 127.0.0.1:2375:2375
  -v /var/run/docker.sock:/var/run/docker.sock:ro
  -v ./rules.txt:/rules.txt:ro
  hectorm/cetusguard -rules-file /rules.txt
Small on purpose
Written in Go, memory-safe, with no dependencies outside the standard library and a codebase short enough to audit properly. For a component that stands in front of the daemon, a small surface is the feature: there is very little between the client and the rules that could be wrong.