Unbound
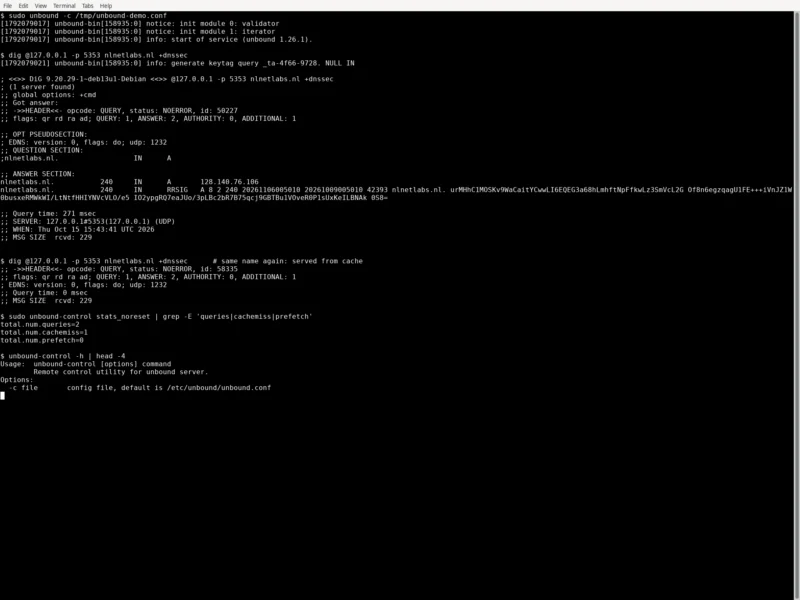
Unbound is a validating, recursive and caching DNS resolver from NLnet Labs, the Amsterdam not-for-profit that also maintains NSD and OpenDNSSEC. Where a conventional name server answers for zones it is authoritative for, Unbound does the opposite job: it takes a query from a client, walks the DNS hierarchy itself from the root down, validates every answer with DNSSEC, and keeps the result in an in-memory cache. It is the resolver you run on a laptop, a router, a home server or a data centre when you would rather ask the nameservers directly than hand every lookup to an ISP or a public resolver. It is written in C for speed and a small footprint, ships under the permissive BSD licence, and is the resolver embedded in the base system of the major BSDs and packaged in every mainstream Linux distribution. The current release is 1.26.1 (September 2026); Debian 13 “trixie” carries it as unbound 1.26.1-0+deb13u1.
Key Features
- Full DNSSEC validation — Unbound fetches the chain of trust from the root down and validates signatures on the way back up, so a tampered or spoofed answer is rejected rather than silently returned. The root trust anchor is maintained automatically with
unbound-anchor, which follows RFC 5011 key rollovers without administrator intervention. - Encrypted transports — DNS-over-TLS and DNS-over-HTTPS let clients encrypt their queries to the resolver, and Unbound can likewise speak DoT/DoH upstream to an authoritative server or forwarder. This is the mechanism behind “privacy DNS” on Android, iOS and in modern browsers.
- Privacy-preserving resolution standards — Query Name Minimisation (RFC 9156) discloses only the part of a name that the server being asked actually needs; the Aggressive Use of DNSSEC-Validated Cache (RFC 8198) lets Unbound answer from NSEC/NSEC3 records it has already validated rather than querying again. Together they cut how much of your browsing leaks to the wider DNS.
- Authority zones and local data — an auth zone (RFC 8806) can hold a local copy of the root zone, and
local-zone/local-dataentries let you serve your own records, blackhole names, or override results for a single machine or a whole network. - Lean, thread-and-event driven core — the packaged build links libevent and runs a small pool of threads with per-thread caches, plus TCP Fast Open for clients and servers. Module support covers DNS64 (NAT64 environments), response policy zones (RPZ), EDNS Client Subnet (
subnetcache), a cache backend for external storage (cachedb, with Redis),dnstapquery logging, and an embedded Python module for scripted behaviour. - Operable from the command line —
unbound-controlreports statistics, flushes or dumps the cache, reloads configuration and manages the running daemon over a local socket;unbound-checkconfvalidates a configuration before it is applied;unbound-hostperforms one-off validated lookups; andlibunboundexposes the same resolver as a library so other software can validate names in-process. - Fine-grained policy — access control lists, views per client subnet, forwarding and stub zones, prefetching of popular names, and
serve-expiredbehaviour are all configuration options, which is why Unbound is the usual recursion engine behind Pi-hole, AdGuard Home and similar filter setups.
Why Use It
The case for running your own resolver is privacy and independence. By default a machine asks whichever resolver its network hands it, which means every hostname it visits is recorded by that operator. Unbound turns that into a direct conversation with the authoritative servers, with QNAME minimisation limiting what each of them learns, and with DNSSEC guaranteeing the answers are genuine. It is also genuinely fast: the cache is in memory, the code path is deliberately small, and a second lookup of the same name is answered locally in microseconds. Because it is packaged everywhere and needs only a few lines of configuration to resolve for a single host or a whole LAN, it is one of the highest-value services a self-hoster can run — and, being BSD-licensed with no account, telemetry or premium tier, there is nothing to outgrow.
Use Cases
- Local recursion for a LAN — run Unbound on the router or a home server and point the network’s DHCP at it, so no upstream provider sees the household’s queries.
- Recursion behind a filter — the standard Pi-hole and AdGuard Home pattern: the blocker answers for the LAN and forwards the names it allows to Unbound, which validates and caches them.
- Privacy DNS endpoint — expose Unbound over DoT or DoH so phones and laptops can encrypt their lookups wherever they are.
- Validating forwarder in an enterprise — place it in front of an existing name server so that internal clients get DNSSEC-validated answers without re-architecting the whole DNS estate.
- Observability — feed
dnstapor theunbound-control statscounters into Prometheus and Grafana to see what a network is actually resolving, and at what cache-hit rate.
Alternatives
- Pi-hole — a network-wide ad and tracker blocker that uses a resolver such as Unbound underneath; it filters, Unbound resolves.
- WireGuard — encrypt the transport; pair it with an encrypted resolver to protect the lookups that travel over it.
- Suricata and CrowdSec — inspect the traffic and block the hosts once DNS has pointed a client at them.
- Prometheus and Grafana — collect and graph Unbound’s statistics alongside the rest of a self-hosted estate.
Platform
Linux, the BSDs (it ships in the base system of FreeBSD, OpenBSD, NetBSD and DragonFly), macOS and other Unix-like systems, with packages in all mainstream distributions · builds from source with a C compiler and OpenSSL, optional libevent, libnghttp2 (DNS-over-HTTPS) and hiredis (Redis cache backend) · typically deployed as a service (systemctl enable --now unbound, apt install unbound) listening on port 53, loopback-only by default in the Debian package.
Licence
BSD-3-Clause (the “New” or “Revised” BSD licence) — free and open source, permissive, with no feature gating, account or paid tier. Development is led by NLnet Labs, a Dutch non-profit; commercial support contracts are offered but are not required for any functionality.
Website
nlnetlabs.nl/projects/unbound · source on GitHub · documentation · also see the Security & Privacy category and the full directory for more tools that keep a network honest.