TruffleHog
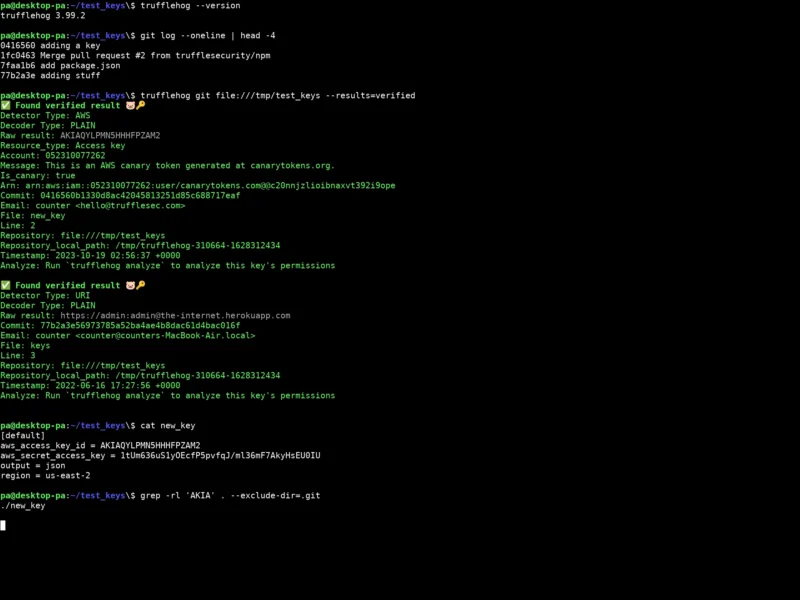
TruffleHog — the open-source secrets scanner from Truffle Security that finds, classifies and, crucially, verifies leaked credentials across git repositories, filesystems, cloud storage, chat and CI — is the tool that turned secret scanning from a grep into a test. Written in Go and released under the AGPL-3.0, it ships more than 900 detectors covering API keys, database passwords, private keys and tokens from AWS, Stripe, Slack, GitHub, Cloudflare, Postgres and hundreds more. The current release is v3.99.2 (October 2026) and the repository is under active development with over 28,000 stars. The project began in 2017 as a Python script that flagged high-entropy strings in git history; the modern v3 is a complete Go rewrite. Its defining idea is verification: for every secret it can classify, TruffleHog can also make a read-only call to the issuing provider’s API to prove the credential is live. A scan therefore returns three kinds of result — verified (confirmed working), unverified (looks like a real secret but could not be confirmed) and unknown — and you can filter to any combination of them.
Key Features
- Verified findings, not just patterns — the scanner attempts a real authentication against the issuing service for every classifiable secret.
--results=verifiedlets you gate a build only on credentials that are provably active, which removes most of the noise that makes regex-only scanners easy to ignore. - More than 900 detectors — each detector is a typed Go implementation with its own keyword set, regex and verification routine, covering everything from AWS access keys and Stripe live keys to Slack tokens, Cloudflare API tokens, PEM private keys, database connection strings and generic JWTs.
- Depth analysis — for around twenty of the most commonly leaked credential types,
trufflehog analyzegoes beyond “is it live?” and reports what the key can actually do: who created it, which resources it reaches and what permissions it holds. - Many sources, one binary —
git(local paths,file://and remote URLs),github(orgs, repos, issue comments and PR comments, plus experimental cross-fork object discovery that enumerates deleted and hidden commits),gitlab,filesystemfor directories and single files,s3,gcs,dockerimages (remote registry, local daemon or a saved tarball),postman,jenkins,elasticsearch,huggingfacemodels/datasets/spaces/buckets,syslog,circleci,travisci,stdinfor piped data, andmulti-scanto describe many sources in one configuration file. - Output a pipeline can use — the default human-readable report,
--jsonfor one JSON object per finding,--sariffor GitHub code scanning (findings appear inline on pull-request diffs and are tracked as new or fixed across runs), and--redactto mask every secret so a report can be shared or logged safely. - Built for CI — an official GitHub Action, a documented GitLab CI job, Docker images published to Docker Hub and ghcr.io, and
--fail, which exits with code 183 when verified credentials are found so a leaking pipeline stops instead of warning. - Pre-commit hook — catch a credential before it ever leaves the workstation, documented in the project’s PreCommit guide.
- Custom regex detectors (alpha) — define your own regex plus keyword and, optionally, a webhook the tool posts candidate matches to: a
200 OKresponse marks the secret verified. Omitting the webhook still reports unverified matches, which makes this useful for genericpassword=andsecret=patterns in.env,.propertiesand YAML files that no built-in detector would catch. - Canary token detection — tokens from canarytokens.org are recognised statically and flagged as canaries, so a deliberate tripwire is not confused with an accidental leak.
- Signed, verifiable releases — every artifact ships with a checksum file signed with Sigstore cosign, and the install script can perform that signature verification for you (
sh -s -- -v). - A funded project, not a side experiment — Truffle Security sells a commercial enterprise offering that continuously monitors Git, Jira, Slack, Confluence, Microsoft Teams and SharePoint; the revenue funds the open-source scanner, and the CLI itself is a complete standalone tool with no licence key, no account and no telemetry.
Why Use TruffleHog?
Leaking a credential is the failure mode that costs the most and is hardest to spot: the code is valid, the tests pass, and the key is simply sitting in a string that was committed months ago and deleted last week. Git history keeps every version of every file, so a key removed in a later commit is still a key somebody can find. TruffleHog answers the two questions that actually matter after a finding appears: is this credential still usable, and if so what can it do? Verification is what separates a result list you triage from a result list you act on — and it is why a scan that reports a single verified finding is far more useful than one reporting two hundred pattern matches. It runs entirely on your own machine or in your own CI, so private and regulated code never leaves your infrastructure; the detectors are readable Go rather than a black box, and the AGPL licence removes the procurement conversation. The trade-off against a purely local pattern scanner such as Gitleaks is a deliberate one: verification means outbound network requests, slower scans on large histories and a dependency on the provider’s API being reachable, so pair --results=verified with unknown when you want both the confident hits and an early warning of secrets that cannot be confirmed.
Use Cases
- Add a pre-commit hook that blocks a credential before it is ever pushed to a remote.
- Gate pull requests in CI: scan the branch delta since
mainwith--results=verified,unknown --failand let the build fail on a live key, uploading SARIF to GitHub code scanning so findings appear on the diff. - Sweep an entire organisation’s GitHub repositories —
trufflehog github --org=<org> --exclude-archived --results=verified— instead of cloning each one by hand. - Audit a repository’s full history before open-sourcing it, handing it to a contractor or onboarding an acquirer.
- Recover deleted and private-repo data:
github-experimental --object-discoveryenumerates hidden and deleted commits so a secret removed by a force-push is still found. - Scan the places credentials are actually forgotten — S3 and GCS buckets, Docker image layers, Elasticsearch indices, Jenkins jobs, Postman workspaces and Hugging Face repos.
- Triage an incident: after a key leaks, establish every commit, file and archive that ever contained it, confirm whether it was live, then rotate with evidence in hand rather than hope.
- Check infrastructure as code and configuration rather than source alone — Terraform, Kubernetes manifests, Docker Compose and
.envfiles are all just filesystem targets. - Read the exposure from a log stream with
trufflehog syslogwhen secrets are being logged rather than committed.
Similar
- Gitleaks — the other major open-source secret scanner. Also from Truffle Security’s orbit, but MIT-licensed, rule-driven and entirely offline: regex plus entropy matching, with no live verification. Reach for Gitleaks when you want a fast, deterministic, network-free gate; reach for TruffleHog when you need to know whether a key is actually live.
- Semgrep — a general-purpose static analyser with a secrets ruleset. Broader than credential hunting (it looks for vulnerable code patterns too), but it matches rather than verifies.
- detect-secrets — Yelp’s plugin-based scanner for Python projects, built around a baseline file and its own entropy heuristics; a natural choice where the workflow is already Python. Not listed in the directory yet.
- Falco, CrowdSec and osquery — runtime counterparts. Those watch a running host or cluster for malicious behaviour; TruffleHog watches repositories and buckets for the credential that would let the attacker in.
Platform
Linux (x86-64, arm64, armv6/armv7) · macOS (Intel and Apple silicon) · Windows (x86-64) · Docker (Docker Hub trufflesecurity/trufflehog and ghcr.io) · Homebrew (brew install trufflehog) · standalone binaries from the releases page · Go toolchain (go install) · official install script with optional cosign verification.
Licence
AGPL-3.0 — the TruffleHog CLI, its detectors and its source. The hosted TruffleHog Enterprise service (continuous scanning of Git, Jira, Slack, Confluence, Teams and SharePoint) is a separate commercial product; using it is not required for anything described above.
Website
source on GitHub · product page · canarytokens.org · also see the Security & Privacy category for more tools that keep secrets and systems in check, or browse the full directory.