Kali Linux
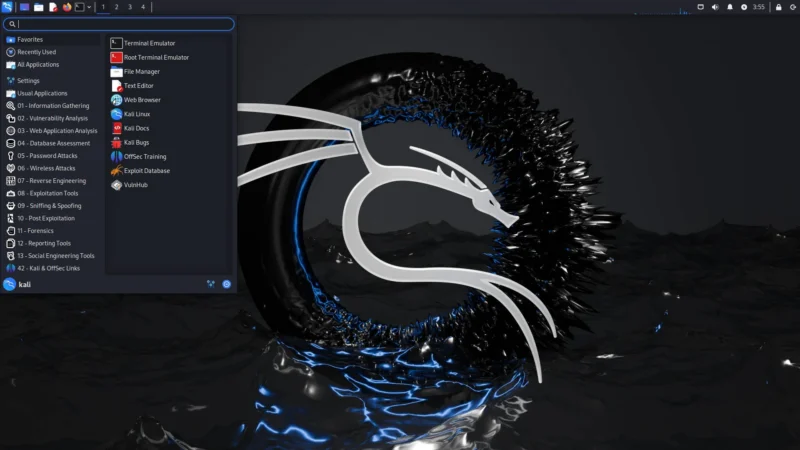
Kali Linux is a Debian-based distribution from Offensive Security, purpose-built for digital forensics and penetration testing. It ships with several hundred pre-installed security tools covering the full assessment workflow — from information gathering and vulnerability analysis to exploitation, wireless attacks and post-exploitation. Rolling, regularly refreshed images keep the toolset current, and it is a fixture in security training, CTFs and professional red-team work.
Key Features
- Purpose-built toolset — several hundred pre-installed tools for every stage of a security assessment
- Debian-based rolling release — built on the Debian testing branch with images refreshed every few months
- Live boot and forensics mode — run from a USB stick or DVD, or in forensics mode that leaves the target untouched
- Metasploit-ready — ships preconfigured with Metasploit, Nmap, Burp Suite, Aircrack-ng, John the Ripper and more
- Broad hardware support — x86-64 and ARM images, including dedicated Raspberry Pi and WSL releases
- Undercover mode — instantly disguise the desktop as Windows to avoid drawing attention during assignments
- Kali NetHunter — a mobile penetration-testing kit for Android devices
- Secure defaults — runs as a non-root user by default with signed packages and isolated tool execution
Why Use Kali Linux?
Kali is the de facto standard operating system for learning and performing penetration testing. Because the whole distribution is oriented around it, you get a coherent, tested environment rather than the patchwork of tools you would assemble by hand. Rolling updates and huge community and video-course coverage make it the easiest serious security OS to pick up.
Use Cases
- Penetration testing and security assessments
- Digital forensics and incident response
- Security research, CTF competitions and bug bounty
- Cybersecurity education and exam practice
Platform
Linux · x86-64 · ARM (including Raspberry Pi)
Licence
GPLv3