Syft
Overview
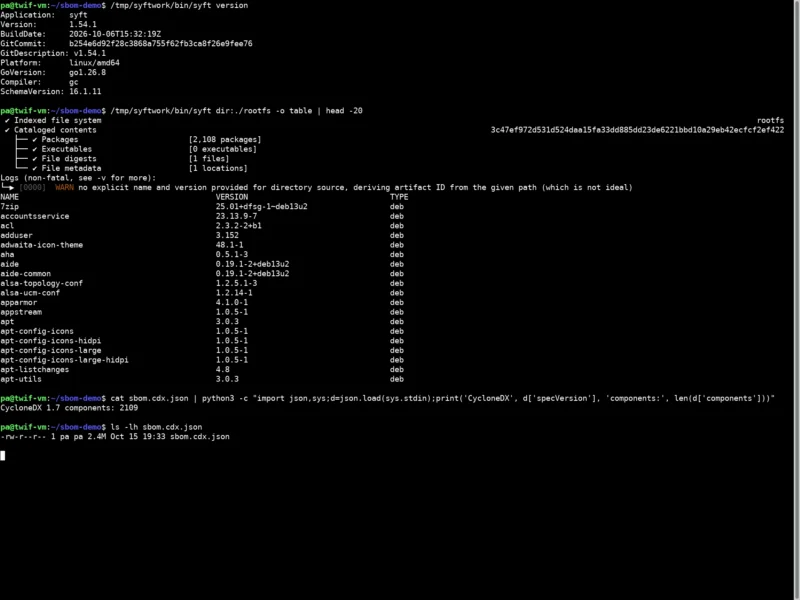
Syft is an open source Software Bill of Materials (SBOM) generator from Anchore, distributed as a single command-line tool and a Go library. It answers a question that has moved from nice-to-have to procurement requirement — “what exactly is inside this container image, filesystem or archive?” — by cataloguing every OS and language package it can identify and emitting the result in a standard, machine-readable format.
Syft is the read side of the Anchore open source toolchain: it produces the inventory, and a scanner such as Grype consumes it to match packages against known vulnerabilities. That split matters in practice. Cataloguing an image is the expensive part of a scan; matching it against a vulnerability database is cheap. Because Syft writes a portable artefact (CycloneDX, SPDX or its own JSON), you can generate the SBOM once at build time, archive or sign it, and then rescan it later without pulling the image again — which is exactly what modern supply-chain compliance workflows ask for.
The project lives at github.com/anchore/syft, is released under Apache-2.0, and is actively developed — the current line is v1.54.1 (October 2026), with roughly 9,700 GitHub stars and documentation hosted at oss.anchore.com.
Key Features
- Many scan targets — container images (OCI, Docker and Singularity formats), arbitrary directories and filesystems, and archives. A whole Debian root filesystem, a project checkout or a saved image tarball can all be catalogued with the same command.
- Broad packaging ecosystem support — dozens of package types are understood, including OS packages (Alpine
apk, Debiandpkg, RPM) and language ecosystems such as Go, Python, Java, JavaScript, Ruby, Rust, PHP and .NET. - Standard SBOM output formats — CycloneDX, SPDX and Syft JSON are produced natively, with additional formats available, and Syft can convert an existing SBOM from one format to another.
- Multiple outputs in one run — several formats can be written simultaneously, to stdout or to named files, so a build can publish a JSON SBOM for tooling and a human-readable table for the log at the same time.
- Signed SBOM attestations — attestations can be created using the in-toto specification, attaching provenance to the inventory rather than shipping an unsigned file.
- Designed to pair with Grype — the README states plainly that Syft is “exceptional for vulnerability detection when used with a scanner like Grype”; both projects are maintained under the same roof.
- Local containers-storage scanning — on Linux, images already sitting in a Buildah or Podman store can be scanned explicitly with
--from containers-storage, including rootless stores viapodman unshare. - One static binary — a self-contained Go program with no agent, daemon, runtime dependency or server component.
Why Use Syft?
SBOM generators have converged on much the same capability set, so the useful question is what Syft does better than the alternatives. Three things stand out. First, breadth of cataloguers: Syft’s package detection is its core competence, and it is continuously extended across distribution formats and language ecosystems, including formats that other tools skip. Second, output fidelity: because it can write CycloneDX and SPDX natively and convert between SBOM formats, Syft fits whatever your downstream tooling already consumes instead of forcing a proprietary schema on you. Third, the pairing with Grype — generating and scanning SBOMs with two tools from the same project means the inventory and the matching logic are tested against each other.
It is also pleasantly unopinionated about where it runs. There is no cloud service, no account, no licence key and no telemetry requirement: Syft is a local binary you point at a target, and it prints an SBOM. For a regulated or air-gapped environment that property alone can decide the choice.
Use Cases
- SBOM generation in CI/CD — produce and archive an SBOM for every built image as a release artefact, giving each version a component inventory that survives long after the image itself is rebuilt.
- Supply-chain compliance — satisfy SBOM requirements from customers and regulators by exporting CycloneDX or SPDX rather than hand-maintained spreadsheets.
- Feeding a vulnerability scanner — catalogue an image once, then let Grype rescan the stored SBOM whenever the vulnerability data is updated.
- Auditing an unfamiliar artefact — inspect exactly which packages a third-party image or vendor archive contains before deploying it.
- Reconnaissance of your own systems — point Syft at a filesystem to inventory everything installed, which is a fast way to find abandoned or unexpected packages on a long-lived host.
- Dependency transparency — combine OS package results with language package results to see the full transitive shape of a project, not just one ecosystem.
Platforms
Syft is written in Go and ships as a static binary for Linux, macOS and Windows, with release builds covering x86-64 and Arm64 as well as Linux ppc64le and RISC-V. It is also distributed as a container image, as .deb and .rpm packages, and through Homebrew, Scoop, Chocolatey and Nix; the install page documents each route. The containers-storage feature is included in the official Linux release binaries — building from source instead requires the containers_image_openpgp,exclude_graphdriver_btrfs build tags.
Licence
Free and open source — Apache-2.0. Verified from the LICENSE file in the GitHub repository and the licence metadata on the project page. Development is sponsored by Anchore, which sells a commercial enterprise platform — but Syft itself is a complete, independently usable tool under Apache-2.0, with no account, API key or paid tier needed to generate SBOMs.
Website
github.com/anchore/syft · documentation & getting-started guide · CLI reference
Related Tools
Syft is the natural companion to Grype for vulnerability scanning and complements broader scanners such as Trivy. Browse the rest of the free and open source security tools in the directory.