Nuclei
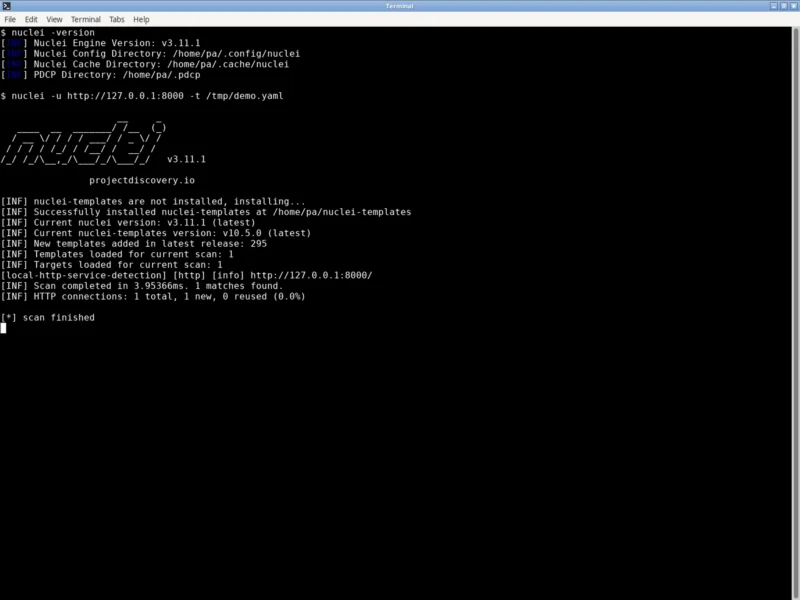
Nuclei — a fast, template-driven vulnerability scanner from ProjectDiscovery — is the tool that turned vulnerability checking from a bespoke scripting exercise into a shared, versioned format. Instead of shipping a monolithic scanner with a fixed rule set, nuclei runs templates: short YAML files that describe the requests to send and the responses that prove a finding. Written in Go under the MIT licence, with roughly 32,000 stars on GitHub, it scans a host, a CIDR range or a list of URLs against the community template library or against your own private templates, and is common enough in the field that many security teams treat it as the default way to check for a newly disclosed vulnerability. The current release is v3.11.1 (August 2026).
Key Features
- YAML templates as the unit of detection — a template declares an id, metadata (name, author, severity, tags), the protocol block to run, and the matchers/extractors that decide whether the response is a hit. Because verification steps are written out explicitly instead of being implied by a signature, a template can simulate the multi-step flow of a real exploit path rather than pattern-matching a banner.
- Eleven protocols, not just HTTP — templates can speak
http,dns,tcp,ssl,websocket,whois,file,headless(a real Chromium browser),code(scripts),javascriptandworkflow; filter a run by protocol with-ptor exclude one with-ept. - The community template library — the
nuclei-templatesrepository is maintained alongside the engine and shipped on first run; templates are filtered by-tags,-severity(info, low, medium, high, critical, unknown) or by author, and updated with-update-templates. Official templates are cryptographically signed, and-dutlets a locked-down run refuse unsigned or tampered templates entirely. - Workflows — a workflow chains several templates and conditions together (
-w,-wurl), so a scan can first fingerprint what a host actually is and then run only the checks relevant to that product. - Fuzzing / DAST mode —
-dastloads fuzzing templates and mutates parameters, paths and headers, with an aggression level (-fa low|medium|high), in-scope regexes (-cs) and a tunable fuzzing mode (-ft,-fm). The same machinery can run as a live DAST server (-dts) or as a proxy in front of your own traffic (-dtp). - Blind and out-of-band detection — built-in Interactsh integration supplies a callback host, so templates can detect blind SSRF, XXE, log4j-style JNDI lookups and other bugs that produce no visible response. Point it at your own server with
-iserver, or switch it off with-ni. - Speed controls that respect the target — parallel processing and request clustering by default, with an explicit
-rlrate limit (150 requests/second default), a per-host mode (-per-host-rate-limit), concurrency (-c), bulk size and timeouts. Template loading can be validated before a run with-validate, and an interrupted scan can be continued with-resume. - Machine-readable output — JSONL (
-j,-jsonl), JSON (-je), SARIF for code-scanning dashboards (-se) and Markdown reports, with-irr/-omit-rawcontrolling whether raw request/response pairs are embedded and-stats-jsonfor live statistics. Findings carry the template id, severity, matched URL and extracted values, which makes them straightforward to triage in bulk. - Flexible target input —
-imaccepts a plain list, a Burp Suite export, JSONL, YAML, OpenAPI/Swagger definitions or raw HTTP requests, so scanning an API’s declared surface is a two-command job. - Fits CI/CD and existing tooling — a single self-contained binary, Docker images, packaged in Debian, installable with
go installor Homebrew, plus documented integrations with Jira, Splunk, GitHub, GitLab and Elastic via the ProjectDiscovery Cloud Platform.
Why Use Nuclei?
The reason nuclei spread so quickly is that it made the detection format the community asset instead of the scanner. When a serious vulnerability lands, what appears within hours is a template — readable, reviewable, and often one screen long — that you can run against your own estate without waiting for a vendor to ship an update or for a scanner to fingerprint your product first. Templates are plain text, so they can be reviewed in a pull request, version-pinned alongside your code and kept private when they describe something you would rather not publish. The engine itself is a single Go binary with no runtime dependencies, so it runs from a laptop, a jump box inside a segmented network or a CI runner with equal ease, and because scans execute locally, target lists and results stay on your own infrastructure. That said, nuclei is a scanner and not an authorisation: it is designed to probe remote systems, and ProjectDiscovery explicitly notes it is built to be used as a standalone CLI tool, warning that running it as a service carries security risks. Point it only at systems you are permitted to test, keep the rate limit sane, and read the release changelog before updating, because the project moves fast.
Use Cases
- Check an estate for a freshly disclosed CVE using the community template by
-id, hours after the advisory rather than weeks. - Run an external attack-surface sweep over a list of subdomains with the safe
infoandlowseverity templates before any active testing begins. - Gate a pipeline: run nuclei against staging in CI and fail the build on a high or critical finding (SARIF output uploads straight into GitHub code scanning).
- Write a private template for a bespoke internal application — a debug endpoint that must never be reachable, an unauthenticated admin path — and re-run it after every deployment as a regression check.
- Scan a network rather than a website: DNS, TCP and SSL templates check zone records, exposed services and TLS configuration.
- Use headless templates where a finding only appears after JavaScript runs, without standing up a separate browser automation stack.
- Fuzz your own application’s parameters with
-dastduring development, when the traffic and the target are both yours.
Similar
- Nikto and Wapiti — classic web vulnerability scanners with their own built-in rule sets; nuclei differs by keeping detections in a shared, editable template language.
- Semgrep — static analysis of your own source code; nuclei examines running systems from the outside.
- sqlmap — deep, automated exploitation of a single vulnerability class, where nuclei aims for fast breadth across many checks.
- Gitleaks — credential hunting in repositories; a natural companion before and after a nuclei scan.
- CrowdSec, Lynis and Snort — runtime defences and host audits, where nuclei is the periodic external check.
Platform
Linux (x86-64, 32-bit x86, arm64, arm) · macOS (Intel and Apple silicon) · Windows (x86-64, arm64) · Docker (Docker Hub and ghcr.io) · Homebrew · Go toolchain, requires Go >= 1.24.2 to build · packaged in Debian and other distributions
Licence
MIT — the nuclei CLI, its engine and the format it uses for templates. The official template library, ProjectDiscovery Cloud Platform and the Pro/Enterprise editions are separate products with their own terms; the free tier of the hosted platform is optional and not required to run the scanner.
Website
projectdiscovery.io · documentation · source on GitHub · nuclei-templates · also see the Security & Privacy category for more tools that keep systems in check.